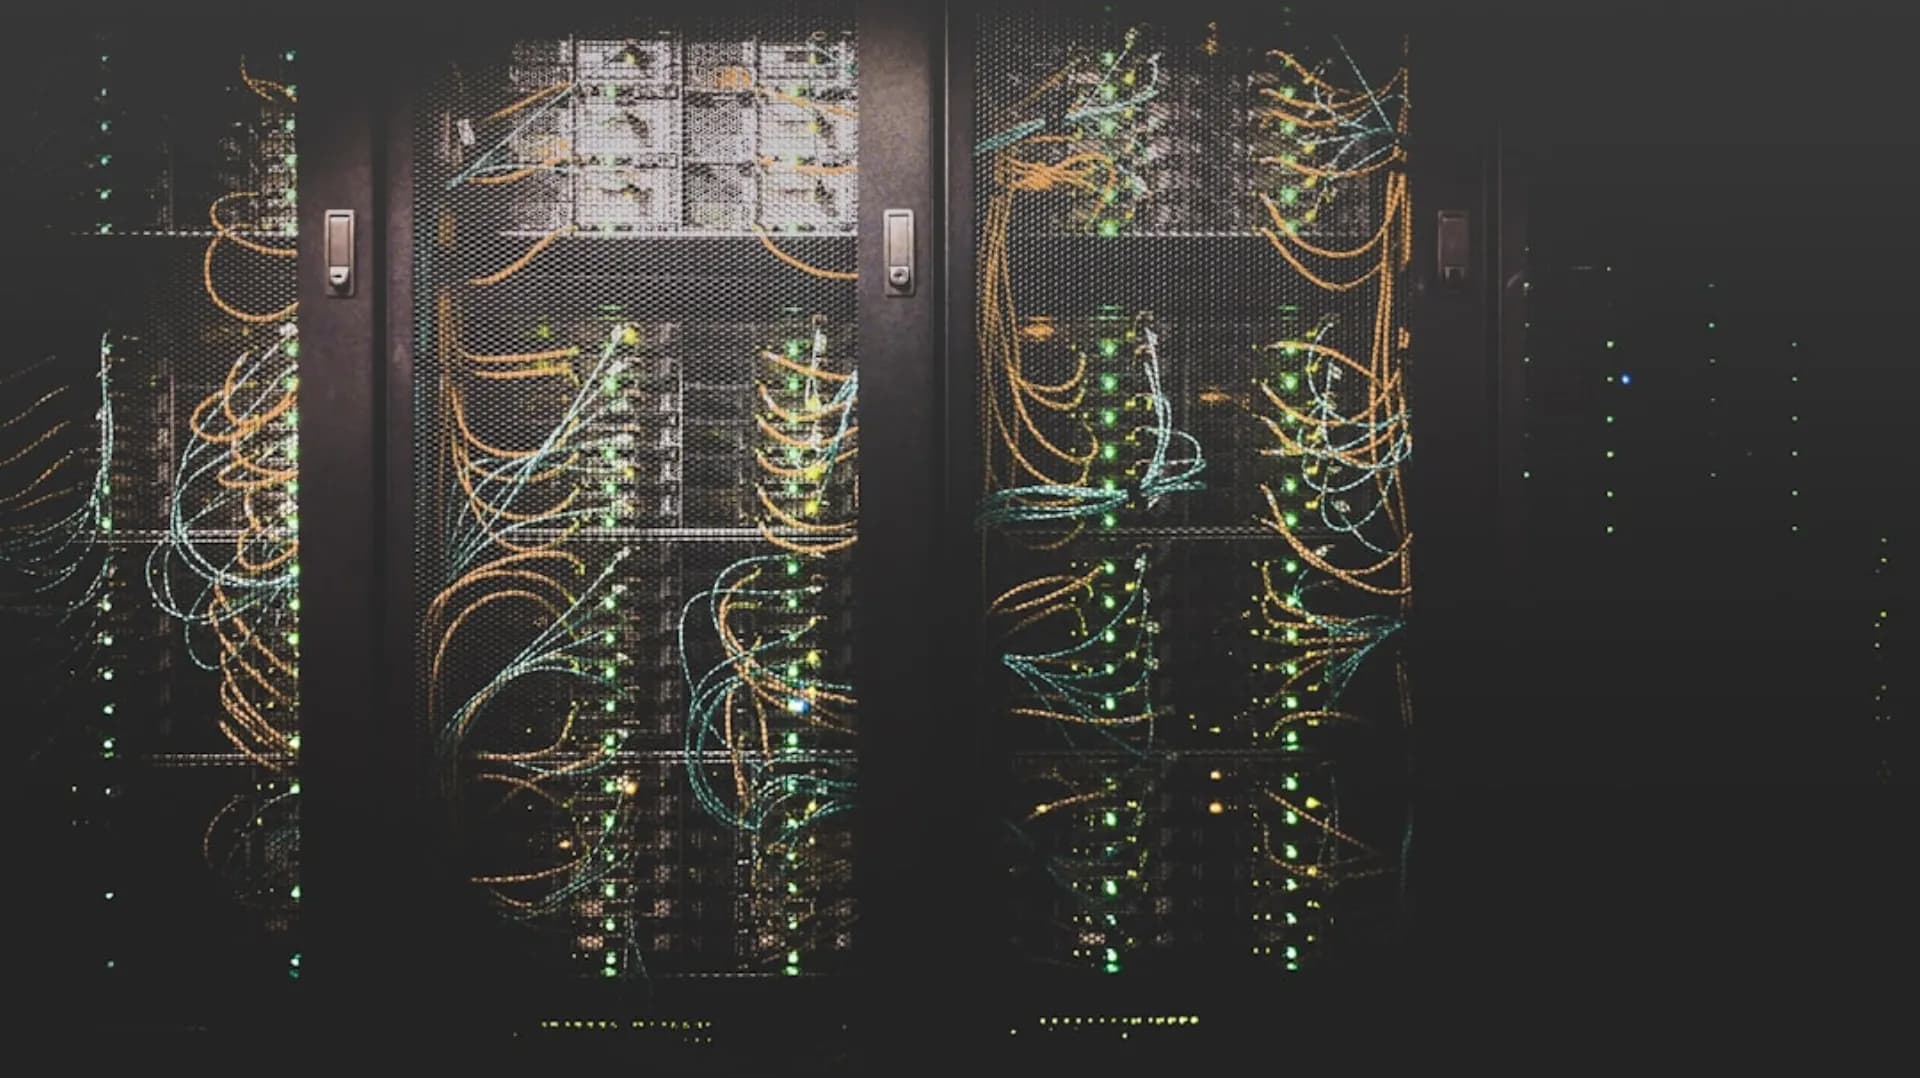
We deployed a self-hosted AI platform over 10 weeks — purpose-built for cybersecurity operations with the absolute data isolation the company required. (1) Air-gapped AI infrastructure. Hardware: 32 NVIDIA H100 80GB GPUs across 4 server nodes, deployed in the company's primary data centre in Equinix SV5 (Santa Clara — the company's existing production infrastructure). Co-located with the company's security data processing pipeline — AI inference occurring within the same security boundary as all other data processing, with no additional data movement. Configuration: 8x H100 per node, 1.5TB system RAM, 24TB NVMe storage, InfiniBand HDR200 interconnect. Network: air-gapped from public internet. Connected only to the company's internal processing network. No API endpoint accessible from outside the company's infrastructure — the AI was an internal service, not an externally accessible system.
Even the company's own employees could not access the AI directly — all interaction through the product's existing security boundary (authenticated, authorised, logged). Security: the AI infrastructure meeting the same security standards as the company's production security data processing — SOC 2 Type II controls, encryption at rest and in transit, access controls, and comprehensive audit logging. (2) Contextual threat detection AI. Attack path analysis: Llama 3 405B fine-tuned on the company's security assessment database (4.2 million cloud configurations from 2,400 customer environments, annotated with security assessment outcomes).
The model learning to identify: multi-step attack paths (a publicly exposed EC2 instance with an unpatched vulnerability, connected to an internal database via overly permissive security group, with cross-account IAM role allowing privilege escalation — each element individually flaggable but the combination representing a critical attack chain that rule-based detection missed), identity-based risks (IAM policies that granted excessive permissions through complex policy combinations — policy A granting S3 access, policy B granting KMS access, combined enabling decryption of all customer data), and temporal patterns (configurations that changed gradually toward insecure states — security group rules accumulating over months, each addition individually approved but collectively creating exposure). Attack path model processing: analysing each customer's cloud environment nightly (complete configuration scan) and identifying critical attack paths ranked by exploitability and potential impact.
Novel attack detection: the model identifying 340 previously unknown attack patterns in the first 6 months — configuration combinations that the company's existing rule set did not cover but that the AI recognised as dangerous based on patterns learned from the broader dataset. These discoveries became new detection rules, improving the product for all customers. Misconfiguration context: the AI distinguishing between: configurations that were genuinely dangerous (immediate remediation required), configurations that were acceptable in context (development environment settings that would be dangerous in production but were appropriate for their current use), and configurations that were technically non-compliant but compensated by other controls (a public S3 bucket that was protected by CloudFront with WAF and signed URLs — technically "public" but effectively protected). This contextual understanding reducing false positive alerts by 42 percent — security teams receiving fewer but more actionable findings. (3) Intelligent vulnerability prioritisation.
Context-aware scoring: the AI combining CVSS base scores with customer-specific context to produce exploitability-adjusted priority scores: network exposure (was the vulnerable system reachable from the internet, from other VPCs, or only locally?), data sensitivity (what data could an attacker access through this vulnerability — classified using the company's data classification model), compensating controls (were there WAF rules, network ACLs, or IAM restrictions that reduced exploitability?), threat intelligence (was there active exploitation of this vulnerability in the wild — correlated with the company's threat intelligence feeds), and blast radius (if exploited, how many other systems and data stores could be reached from the compromised system?). Prioritisation impact: customers' security teams now fixing the most impactful 5 percent of vulnerabilities first — reducing actual security risk by 68 percent while only remediating 140 vulnerabilities (versus unfocused approach of remediating hundreds with uncertain impact).
Automated remediation: for low-risk, well-understood remediations (specific security group rule removals, S3 bucket policy corrections, encryption enablement), the AI generating remediation code (CloudFormation, Terraform, AWS CLI) that security teams could review and execute — or auto-apply for customer-approved remediation categories. 34 percent of vulnerabilities auto-remediable (with customer approval and guardrails). (4) Security copilot: natural language security analysis. Model: Llama 3 70B fine-tuned on: the company's security assessment methodology (how the company's security researchers evaluated cloud configurations), 28,000 customer support interactions (how security analysts asked questions and what answers they needed), cloud provider documentation (AWS, Azure, GCP security documentation — enabling the model to explain configurations with reference to provider-specific concepts), and compliance frameworks (SOC 2, PCI DSS, HIPAA, ISO 27001, CIS Benchmarks — enabling the model to explain compliance gaps with specific framework references).
Natural language querying: security analysts could ask questions in plain English: "Which of our S3 buckets contain PII and are accessible from outside the VPC?" — the AI querying the customer's configuration data and returning specific, actionable results. "What changed in our production environment last week that could affect our PCI compliance?" — the AI correlating configuration changes with PCI DSS requirements and highlighting relevant changes. "Explain why this IAM role is flagged as risky" — the AI providing detailed analysis of the specific policy statements, their effective permissions, and the attack scenarios they enabled.
Incident investigation: when a security alert fired, the AI providing: incident summary (what happened, based on the alert and surrounding events), blast radius assessment (what systems and data were potentially affected), investigation guidance (what logs to check, what configurations to verify, what indicators of compromise to look for), and remediation recommendation (specific steps to contain and resolve the incident). Security architect review: before deploying infrastructure changes, teams could ask the AI to review Terraform or CloudFormation templates: "Review this Terraform plan for security issues" — the AI identifying misconfigurations, missing encryption, overly permissive access, and compliance violations before deployment. (5) SOX and IPO preparation.
AI governance: comprehensive documentation of AI system architecture, data flows, model governance, and security controls — designed for: SOC 2 audit (the company's SOC 2 Type II audit covering AI systems — auditors able to examine AI data handling, access controls, and processing documentation), customer security assessments (enterprise customers conducting vendor security assessments — clear documentation showing that customer data was processed only on the company's infrastructure with no third-party AI provider involvement), S-1 risk factor disclosure (preparing for IPO, the company's legal team reviewing AI risk factors — self-hosted deployment significantly simplifying risk disclosure compared to third-party AI dependency), and SOX preparation (financial AI applications — revenue forecasting, usage analytics — meeting SOX auditability requirements through self-hosted deployment with comprehensive audit trails).